Letter XXII: Provider, Provide — Do Not Prescribe

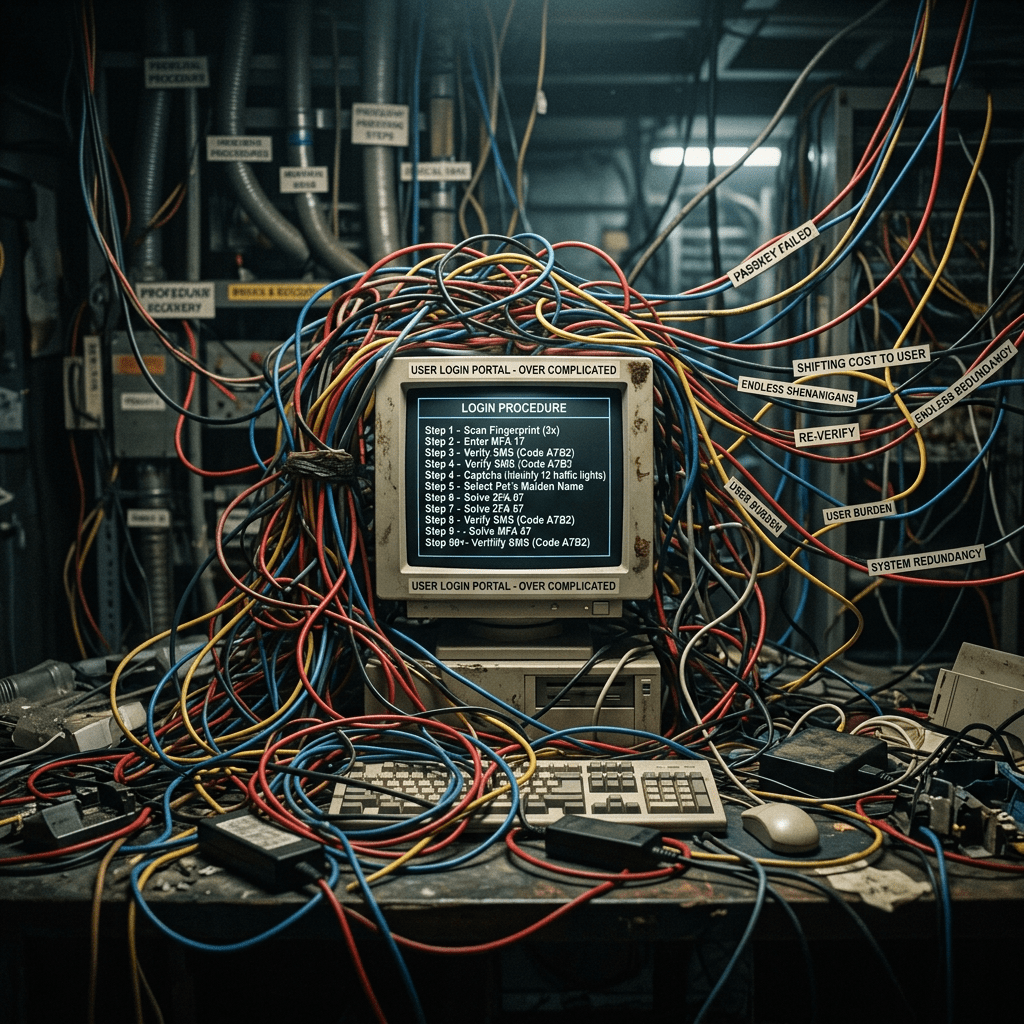
Monitor labeled USER LOGIN PORTAL - OVER COMPLICATED displays ten-step login procedure; tangled cables labeled PASSKEY FAILED, RE-VERIFY, USER BURDEN, and SYSTEM REDUNDANCY surround it.

By Martyn Walker
Published in Letters from a Nation in Decline

This morning, I attempted to log in to a different company account on QuickBooks.

It should have taken perhaps ten seconds. Instead, passkeys turned it into an intense five-to-ten-minute project involving repeated attempts, rejected routes and the usual digital guessing game in which the customer must discover what the software has decided to do on his behalf.

Eventually I checked the settings which I had previously disabled. They had somehow been re-enabled. I had not changed them. Perhaps an update had restored the provider’s preferred defaults; perhaps some other piece of helpful automation had intervened. Either way, my expressed choice had not survived.

A setting which silently reverses itself is not a setting. It is a temporary stay of execution.

Passkeys are presented as the civilised successor to passwords: simpler, safer and resistant to phishing. The cryptography is undoubtedly clever. A passkey is tied to the genuine website and cannot be handed innocently to a convincing imitation. This tackles a real problem, particularly among people who reuse memorable passwords or type credentials into whatever page appears before them.

But the sales pitch quietly substitutes one security problem for another. It concentrates identity, authentication and often account recovery in the same small object carried everywhere in a pocket.

Put down an unlocked telephone and someone else can pick it up. Phones are snatched from people’s hands by thieves on bicycles. Criminals observe PINs before stealing devices. Ministers, officials and businesspeople have all demonstrated that possession of an important telephone is not a theoretical risk confined to careless teenagers. Yet the technology industry increasingly treats possession of the device, assisted by a face, fingerprint or short PIN, as proof of possession of the identity.

The answer from security specialists is that a properly locked telephone still requires biometric or PIN verification. This is true in the same way that a properly locked front door keeps out a burglar who has neither the key nor a window. It describes the security model while avoiding the circumstances in which the security actually fails.

Once a thief gains access to a phone, he may acquire the passkey, email account, text messages, authenticator, password-reset route and banking applications together. We are told this is multifactor authentication. Physically, it is often several differently named functions living inside one stolen box.

I have used Bitwarden since its early days. I do not know any of my account passwords. Each is unique and generated by the password manager; I know only my personal master password. I have never been hacked. My family know that master password, so when I die they will be able to gain access to the accounts and information they will need.

That is not an accidental arrangement devised for my convenience. It is a considered security and succession policy. It has one deliberate trust anchor, controlled by me, with a comprehensible route for inheritance.

Passkeys intrude upon that arrangement by creating a parallel collection of credentials distributed among Apple, Google, individual devices, browser profiles, password managers and service providers. Some synchronise; some do not. Some can be deleted; some appear again. Some sites remember the right account; others offer a passkey for the wrong one. Death, incapacity, loss of a device or a disputed cloud account can turn the promised simplicity into an archaeological expedition through systems nobody consciously chose.

This is not merely an objection to passkeys. Those who want them should be free to use them. The objection is to prescription disguised as provision: automatic creation, persistent prompting, passkey-first login screens and updates which restore settings the customer has already rejected.

The provider benefits handsomely. Fewer forgotten-password calls reduce support costs. Phishing losses decline. Authentication is outsourced to devices and platform companies. The customer supposedly receives convenience, but when the machinery fails, the provider’s saving becomes the customer’s unpaid labour.

Multiply my lost five or ten minutes by millions of users, then add every compulsory application, broken identity portal, circular chatbot, unexplained verification request and setting restored after an update. None appears in the national accounts as waste. It is simply removed from the productive day in fragments too small to invoice and too dispersed to attract ministerial attention.

Britain can no longer indulge this casually. As Ross Clark puts it with admirable economy in the title of his forthcoming book, Britain Is Bust. His subject is the approaching sovereign debt crisis and the unavoidable rationalisation of public spending. Passkeys will neither cause nor cure that crisis. They are, however, a neat specimen of the culture accompanying it: institutions lower their own visible costs by exporting effort, delay and frustration to citizens and businesses, then call the result innovation.

A country does not become unproductive only through grand strategic errors. It also does so ten minutes at a time.

The proper policy is neither difficult nor technologically reactionary. Providers should offer passwords, independent authenticator applications, physical security keys and passkeys. They should explain the differences. They should allow the customer to choose. A rejected method should remain rejected, and an update should not constitute fresh consent. No credential should be created silently. No customer should be repeatedly funnelled towards the provider’s cheapest option.

Security should also permit genuine separation. The credential, the device approving its use and the route for recovery need not all occupy the same phone. People handling valuable businesses or sensitive information should be able to keep authentication on a separate device or physical key. Those planning sensibly for death or incapacity should not have their arrangements defeated by credentials imprisoned inside a dead person’s biometric ecosystem.

The password was not perfect. Neither is the passkey. The difference is that I was permitted to manage the former intelligently, whereas the latter is increasingly imposed upon me by organisations convinced that their preferred system must also be mine.

Let providers provide. Let customers decide. And when we have decided, leave the bloody setting alone.

Letter XI – Press One for Betrayal

By Martyn Walker
Published in Letters from a Nation in Decline

The modern call centre was not designed to solve your problem. It was designed to make your problem someone else’s responsibility.

There was a time—not so long ago—when you could pick up the telephone and speak to someone in authority. Not a chatbot, not an overseas “operative,” not an algorithm tasked with guessing which service category most closely matched the thing that was bothering him. A human being. On the premises. With some measure of agency. One might even call it customer service—a phrase now drained of meaning, like so much corporate jargon turned to husk.

It’s easy to sentimentalise the past, but this isn’t nostalgia. It’s an observation. In 1980, if I had a query about a spare part, a refund, or a change to an order, I called the shop. The shop answered. A man in a brown coat wiped his hands and told me the truth. Perhaps he had to check in the storeroom. Perhaps he said no. But he said something. And I was no longer in doubt.

Now, try calling your local Halfords. Or Sainsbury’s. Or Currys. You’ll search for a phone number, find what looks like a local line, dial it with hope—and find yourself deep in the circuitry of a call centre. Often abroad. The voice will be polite, inoffensive, robotic. And its sole mission is to extract your details. Your name, postcode, date of birth, your grievance if you’re lucky. But it cannot solve your problem. It may not even understand it. You are not speaking to someone in the branch. You are speaking to data acquisition software in human form.

This isn’t a bug. It is the design. You, dear customer, are not a person but a unit of behavioural metadata. A record to be “triaged,” escalated, or dropped. The goal is not to help you but to contain you. Hold times, circular menus, dead-end email addresses, disappearing contact forms—these are not symptoms of strained service, but strategies of avoidance. No longer is the customer always right. The customer is barely relevant.

And when you finally breach the firewall—after ten minutes of hold music and a few weak apologies—you’re passed back, with luck, to the store you originally tried to reach. Or worse, told they “can’t connect you but will raise a ticket.” The circle begins again.

This model of service has metastasised. The state has adopted it with vigour. HMRC—an organisation I once respected—now behaves like a digital fortress. I have owed them money and seen the efficiency with which they communicate. But now they owe me a refund—one triggered at the height of the pandemic, over four years ago—and they are unreachable. My letters go unanswered. Emails are met with silence. Phone calls are looped through menus that lead nowhere. I cannot speak to anyone. And yet, if I were late in payment, I have no doubt I would be found [1].

We are told that these systems are more efficient. That technology has made things easier. That chatbots, web portals, apps, and ticketing systems have replaced “old-fashioned” service with something faster and more scalable. But these are lies. The system is not more efficient—it is more opaque. More exhausting. The problem is no longer one of supply, or of timing, but of deliberate misdirection.

You are meant to give up. That is the efficiency: your defeat.

The corporations know you have nowhere else to go. Tesco boasts of “price matching” against Aldi or Lidl, but only for items carefully selected as competitive loss leaders [2]. The supermarkets function as a cartel in all but name. There is no real price war—only a performance of it. And when every supplier adopts the same approach to service—offshored, automated, evasive—what alternative is left? Who do you reward with your custom?

The human voice—the oldest tool in commerce—is now treated as a cost centre. Empathy is expensive. Initiative is a risk. It is far safer, from a boardroom perspective, to channel all contact into a data funnel, log the frustration, and offer a £5 voucher once a month to appear caring.

Meanwhile, the consumer—the citizen, the taxpayer—is left howling into the void. Asking not even for special treatment, but for the basic reciprocity that once governed civil society.

And so I write this not as a technophobe—far from it—but as someone who sees the difference between progress and abandonment. We have not been “streamlined” into a new age of customer empowerment. We have been reduced. Stripped of our right to a voice, replaced with a row of dropdown menus and a number on a dashboard.

What has died is not merely service. It is the principle of response.

And without response, there can be no trust.

References

  1. National Audit Office (2022). Customer Service Performance at HMRC. NAO report showing average call waiting times exceeding 20 minutes, with some refund cases unresolved after more than a year.
  2. Competition & Markets Authority (CMA), 2023. Supermarket Price Competition Review. The report notes that “price match” campaigns often use cherry-picked items, typically loss leaders, creating an illusion of parity while overall basket prices diverge.
  3. Citizens Advice Bureau (2021). The Customer Service Crisis. Documenting the shift to automated and offshore customer service in key industries and its impact on vulnerable groups.
  4. Financial Times (2023). Retailers’ use of behavioural data surpasses customer service investment. A feature highlighting that major UK retailers spend significantly more on data analytics than on staff training or customer resolution.
  5. House of Commons Treasury Committee (2024). Digital Services and the Decline of Public Accountability. Evidence submitted to Parliament showing the impact of digital interfaces on HMRC accountability and customer complaints handling.

Metadata

Title: Press One for Betrayal
Series Title: Letters from a Nation in Decline
Series Volume: Letter XI
Author: Martyn Walker
Language: English (UK)
Date of Publication: 2025-04-16
Edition: First
Abstract / Short Description:
An essay on the erosion of human-centred customer service in modern Britain, revealing how citizens are now treated as data points, not people. Through sharp satire and lived experience, Press One for Betrayal confronts the state and corporate sectors’ weaponisation of digital systems to deflect responsibility and suppress contact. The personal becomes political in this eleventh letter from a nation in visible decline.


BISAC Subject Headings (Book Industry Standards and Communications):

  • SOC026000 – Social Science / Sociology / General
  • BUS070060 – Business & Economics / Customer Relations
  • POL023000 – Political Science / Public Policy / Economic Policy
  • TEC003070 – Technology / Social Aspects
  • COM087000 – Computers / Human-Computer Interaction

LCSH (Library of Congress Subject Headings):

  • Customer services—Great Britain
  • Call centers—Great Britain
  • Public administration—Effect of technological innovations on—Great Britain
  • Data protection—Great Britain
  • Communication—Technological innovations—Social aspects—Great Britain
  • Administrative agencies—Great Britain—Public opinion
  • Surveillance capitalism—Great Britain
  • Government accountability—Great Britain

Keywords / Tags for Indexing:

customer service, HMRC, UK bureaucracy, call centres, digital inefficiency, datafication, corporate indifference, public sector decay, satire, Letters from a Nation in Decline